Evidence a notified body accepted
Every change to validated software needed a traceable reviewer, a documented rationale and a signature.
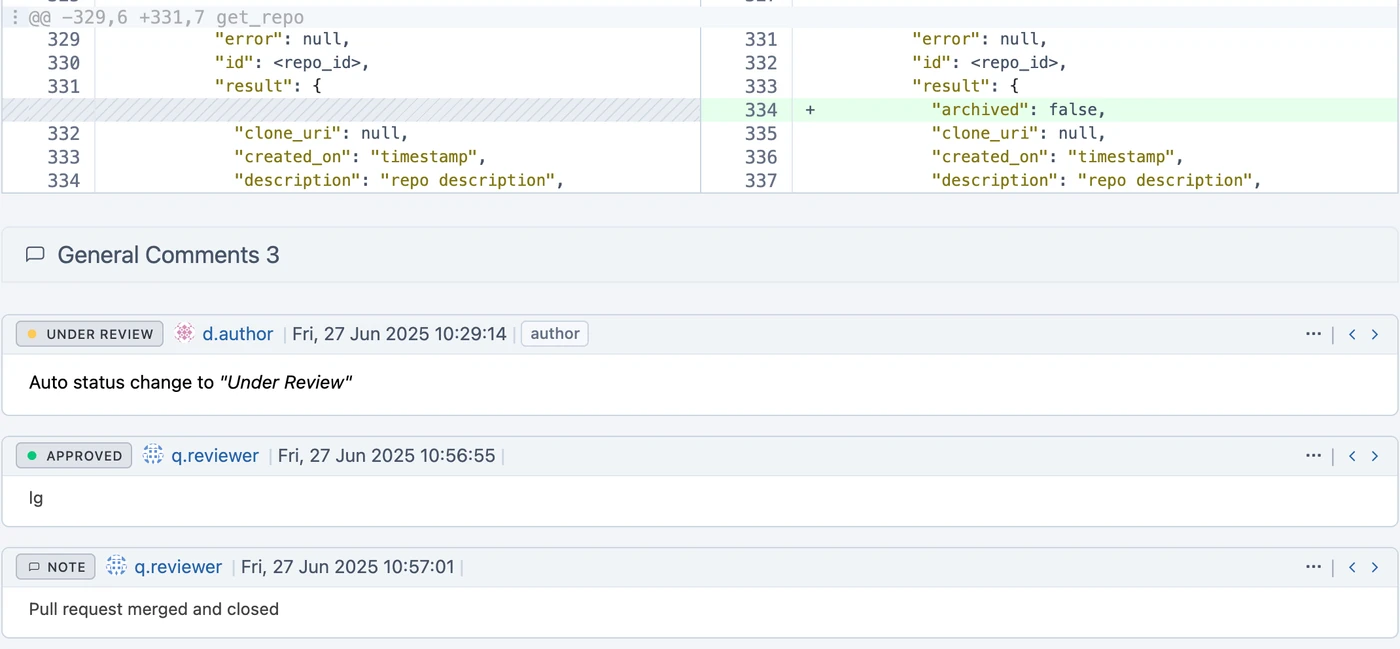
- Signed merges
- 100%
- Modules
- 24
- Export
- Per release
Reviews happened. Proving it was the project.
The reviews were being done properly — the difficulty was producing evidence in a form a notified body would accept, per release, without a manual audit each time.
The existing answer was a spreadsheet assembled by a quality engineer over several days per submission.
Encode the device modules as reviewer rules.
Each of the twenty-four device modules became a path-based reviewer rule with a required approval count, so the right owners are assigned automatically and the merge stays blocked until the rule is satisfied.
Signed commits were enforced on protected branches, making the signature a property of the history rather than a claim about it.
Approval evidence stopped being a project and became an export.
Every merge carries signed approval.
- 00100% of merges carry signed approval
- 0124 device modules encoded as reviewer rules
- 02Approval evidence exported per release
- 03Explicit deny used for contractor offboarding
Submission evidence is generated per release from the platform itself, with reviewer, rationale and signature attached to each change.
Would this approach fit your organisation?
Bring your repository count, your VCS mix and your compliance constraints. We will tell you honestly whether a staged migration is the right answer for you — sometimes it is not.
- Bring
- repository count, VCS mix, seat count
- Constraints
- regulator, classification, contract
- We answer
- within 24 hours, by an engineer
- Contact
- sales@rhodecode.com